




 India
 USA
 UK
 Saudi Arabia
 UAE
 France
 Spain
 Germany
Security Analytics and SOC Modernization with ConsultEdge Global | Gurucul Solutions Partner
ConsultEdge Global helps organizations modernize security operations, detect sophisticated threats, identify insider risks, and strengthen identity security. We support the evaluation, implementation, integration, and optimization of Gurucul's AI-powered security analytics and risk management solutions, aligning the technology with each organization's security and operational requirements.
Gurucul combines AI-driven security , behavioral intelligence, risk scoring, and automation to help security teams detect anomalous activity, investigate threats, prioritize risks, and accelerate response across users, identities, machines, applications, and data.
With Gurucul solutions, organizations can modernize their SIEM, strengthen insider-risk management, improve identity threat detection, automate security operations, and augment SOC teams with AI-assisted investigation and response.
Modernize security operations with Gurucul Next-Gen SIEM. We help organizations centralize security visibility, analyze security data, detect threats, and accelerate investigation through AI-native security analytics and behavioral intelligence.
Gurucul Next-Gen SIEM supports modern SOC environments with flexible data management, advanced analytics, risk-based detection, and deployment options designed for evolving security requirements.
Capabilities available through Gurucul Next-Gen SIEM:
- AI-Native Security Analytics to analyze security data and identify potential threats.
- Behavioral Analytics to detect deviations from established user and entity behavior.
- Native Data-Pipeline Management to streamline security data ingestion and processing.
- Flexible Data-Lake Architecture to support scalable security analytics.
- Centralized Security Monitoring to improve SOC visibility across security environments.
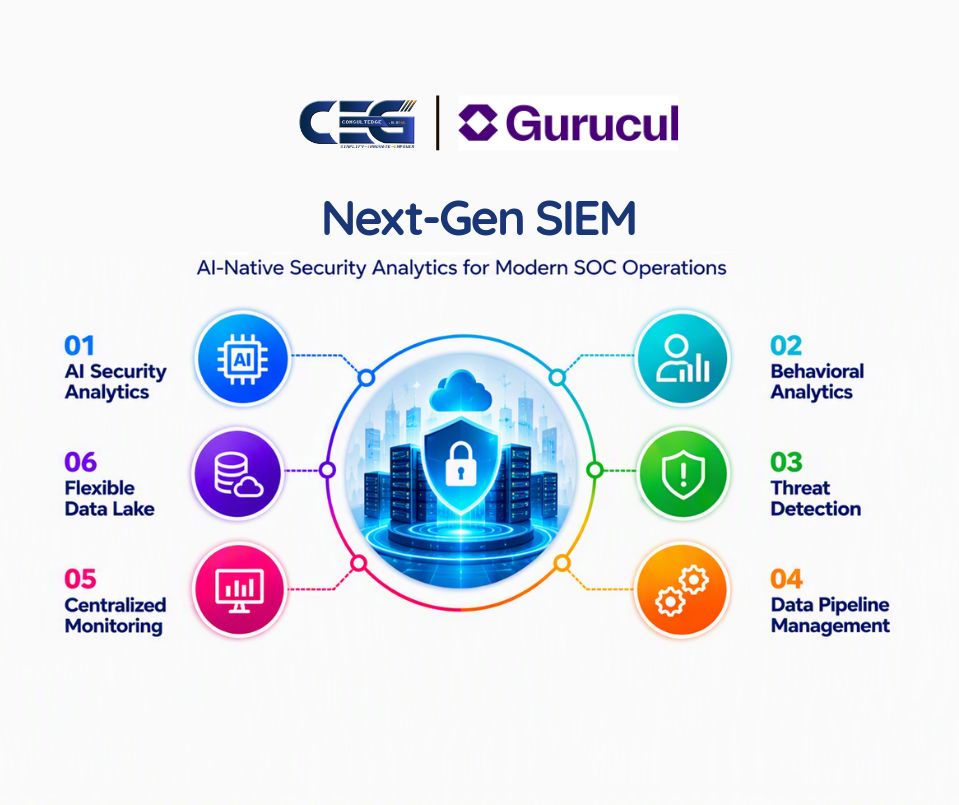
SIEM Modernisation & Security Monitoring Capabilities
Strengthen threat detection with Gurucul User and Entity Behavior Analytics (UEBA). We help organizations identify unusual behavior, compromised accounts, insider risks, and identity-related threats through behavioral baselining and dynamic risk analysis.
Gurucul UEBA analyzes activity across users and machines to provide contextual intelligence and help security teams prioritize high-risk events.
Capabilities available through Gurucul UEBA:
- Behavior Baselining to establish normal activity patterns.
- Anomaly Detection to identify deviations from expected behavior.
- Dynamic Risk Scoring to prioritize users and entities based on risk.
- Entity Intelligence to provide contextual security insights.
- User & Machine Analytics to analyze behavior across different entities.
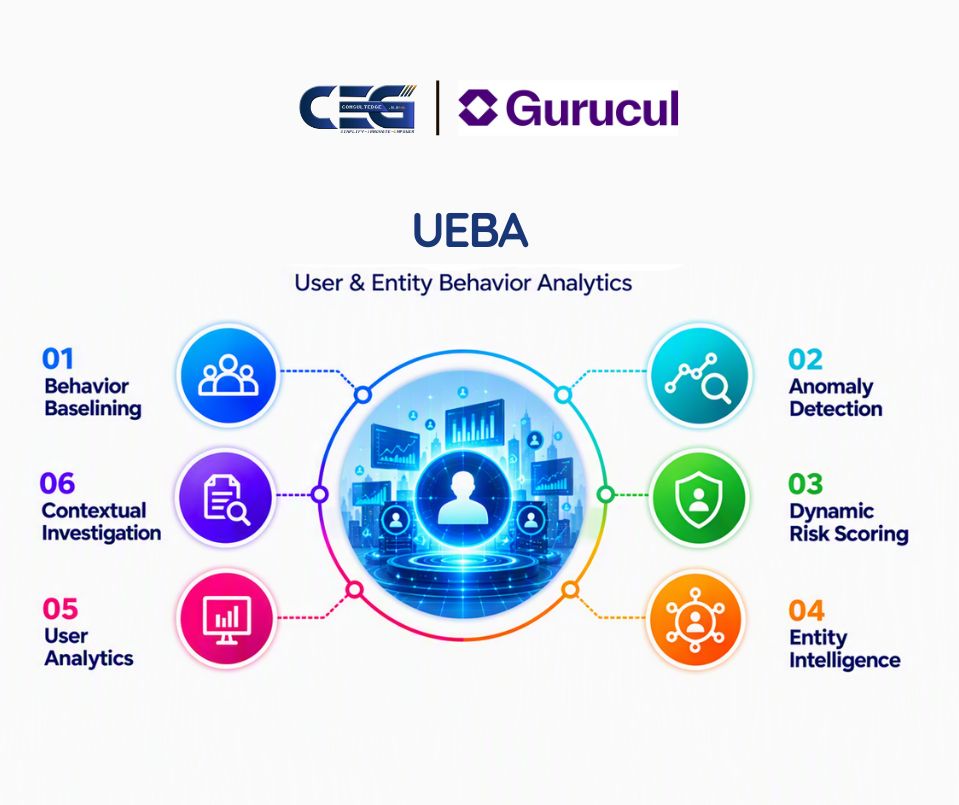
User & Entity Behaviour Analytics Capabilities
Strengthen protection against insider threats with Gurucul AI-Powered Insider Risk Management. We help organizations identify risky user behavior, detect potential data exfiltration, monitor privilege abuse, and support proactive insider-risk investigations.
Gurucul combines behavioral analytics and AI-supported risk analysis to help organizations identify and manage insider-risk signals while supporting privacy and access controls.
Capabilities available through Gurucul Insider Risk Management:
- Insider-Risk Detection to identify potentially risky user behavior.
- Data-Exfiltration Monitoring to detect suspicious movement of sensitive information.
- Privilege-Abuse Detection to identify potentially inappropriate privileged activity.
- AI-Supported Triage to help security teams prioritize insider-risk events.
- Real-Time Controls to support timely risk response.
- Privacy & Access Controls to support responsible insider-risk management.
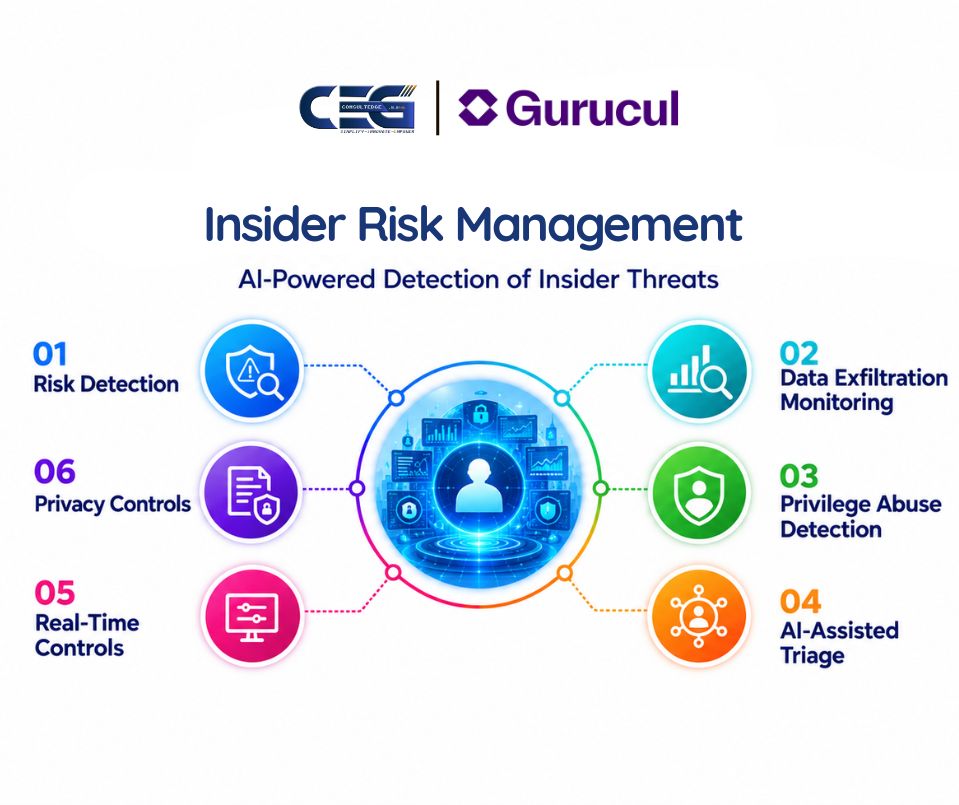
Insider Threat & Data Exfiltration Detection Capabilities
Strengthen identity security with Gurucul Identity Analytics. We help organizations gain visibility into identities, privileges, entitlements, and access risks across hybrid environments.
Identity Analytics supports risk-based identity monitoring and helps security teams identify excessive privileges, entitlement risks, and potentially compromised identities.
Capabilities available through Gurucul Identity Analytics:
- Identity Threat Detection to identify suspicious identity activity.
- Privilege Monitoring to improve visibility into privileged access.
- Entitlement-Risk Analysis to identify potentially excessive or risky access.
- Dynamic Identity Risk Scoring to prioritize identity-related risks.
- Access Review Support to improve visibility into user access.
- Zero Trust Enablement to support identity-centric security strategies.
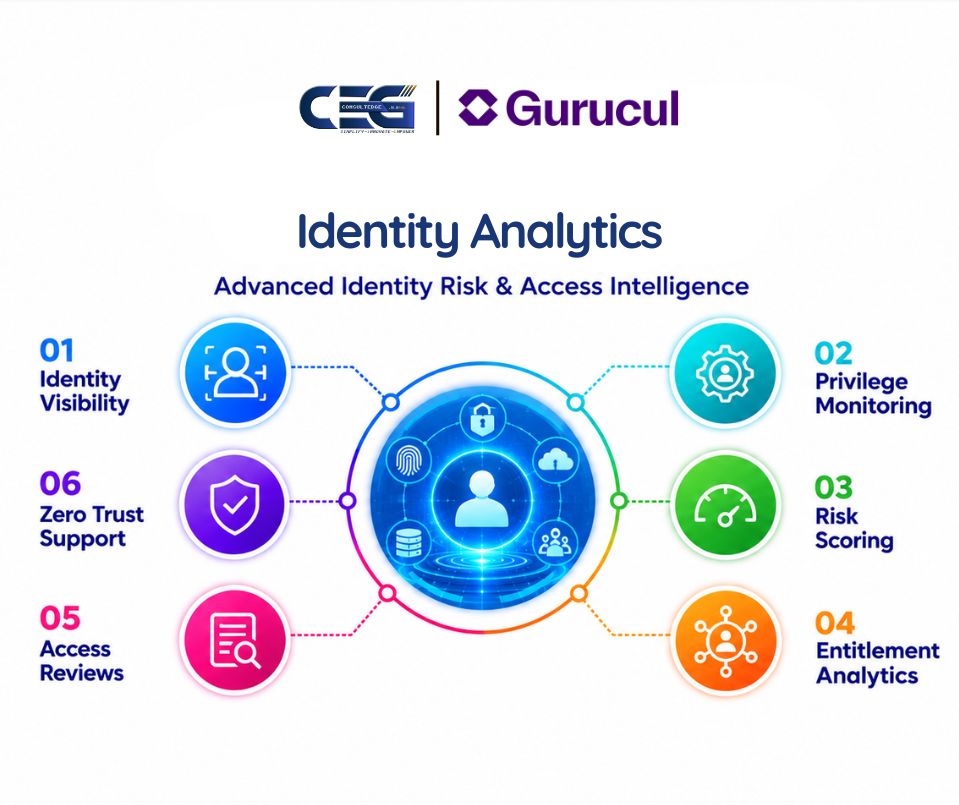
Identity Risk & Access Analytics Capabilities
Accelerate incident response with Gurucul Security Orchestration, Automation and Response (SOAR). We help security teams automate repetitive response activities, enrich investigations, orchestrate workflows, and coordinate security actions across their technology environment.
Gurucul SOAR enables organizations to build customizable response workflows that support faster triage, investigation, containment, and remediation.
Capabilities available through Gurucul SOAR:
- Automated Triage to accelerate initial alert analysis.
- Customizable Playbooks to standardize security workflows.
- Threat-Intelligence Enrichment to add context to investigations.
- Investigation Timelines to support incident analysis.
- Coordinated Response Actions across security tools and teams.
- Automated Containment & Remediation to accelerate incident response.
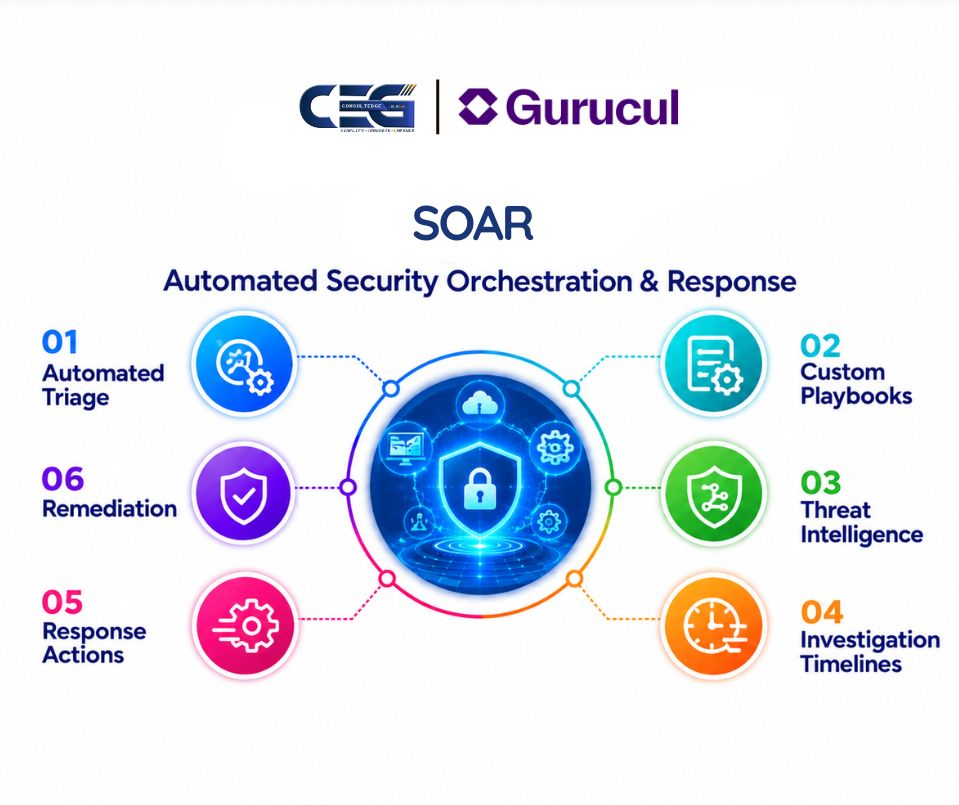
Security Automation & Incident Response Capabilities
Augment security operations with the Gurucul AI SOC Analyst. We help security teams accelerate alert investigation, enrich incidents with behavioral context, and improve analyst productivity through AI-assisted security operations.
The AI SOC Analyst supports SOC teams by helping investigate alerts, correlate relevant context, enrich incidents, and accelerate response while maintaining transparent response actions.
Capabilities available through Gurucul AI SOC Analyst:
- AI-Assisted Alert Triage to help prioritize security alerts.
- Automated Investigation Support to accelerate incident analysis.
- Behavioral Context to improve understanding of user and entity activity.
- Incident Enrichment to provide additional investigation context.
- Response Acceleration to help security teams act faster.
- Security Tool Integration across SIEM, SOAR, EDR, and cloud security platforms.
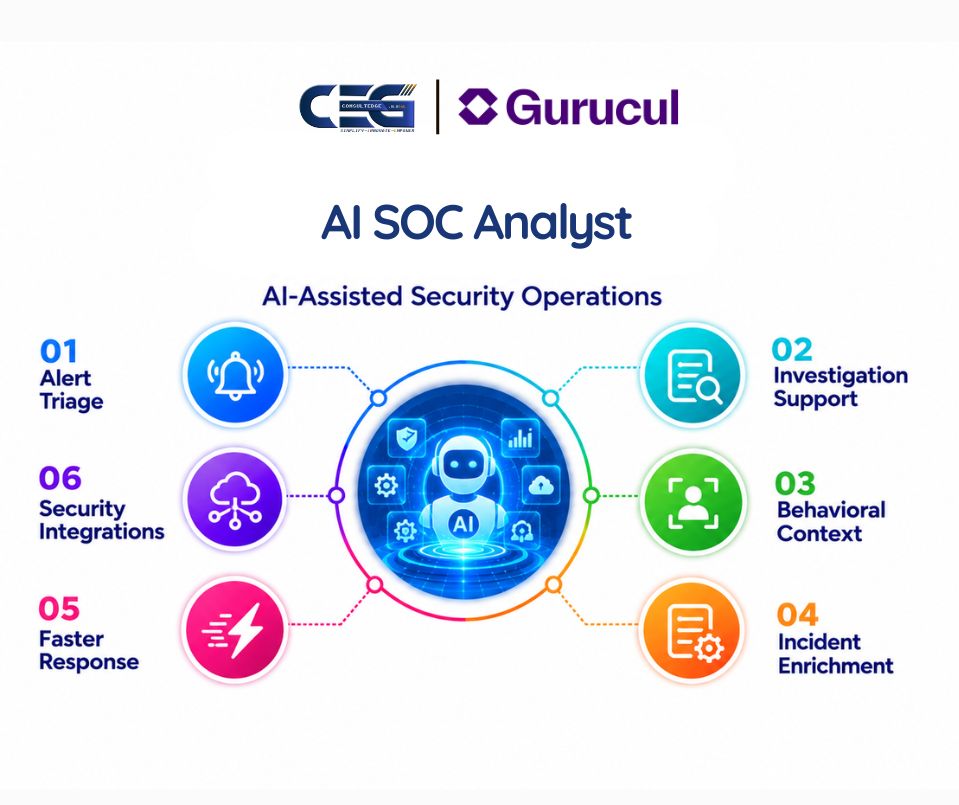
AI-Assisted SOC & Alert Investigation Capabilities
Comprehensive Gurucul Solutions for Modern Security Operations

AI-Powered Security Analytics | Behavioral Intelligence | Insider Risk | Identity Security | SOC Automation
Organizations face increasingly complex security environments involving identities, users, endpoints, applications, cloud platforms, and sensitive data. Traditional security monitoring alone may not provide the behavioral context and risk intelligence required to identify sophisticated threats.
Gurucul brings together AI-powered security analytics, UEBA, insider risk management, identity analytics, SOAR, and AI-assisted SOC capabilities to help organizations improve detection, investigation, risk prioritization, and response.
As a Gurucul Solutions Partner, ConsultEdge Global helps businesses evaluate, implement, integrate, and optimize Gurucul technologies based on their security and operational requirements.
Enquire NowSecurity Solutions by Business Requirement
SIEM Modernisation & Security Monitoring
- Security Monitoring: Centralize security visibility across environments.
- Threat Detection: Identify potential threats using AI-powered analytics.
- SIEM Modernization: Modernize traditional security information and event management.
- Compliance Monitoring: Support security monitoring and compliance requirements.
- SOC Visibility: Improve visibility across security operations.
User & Entity Behaviour Analytics (UEBA)
- Compromised Account Detection: Identify unusual activity associated with potentially compromised accounts.
- Anomalous Behavior Detection: Detect deviations from normal behavior.
- Identity Risk Analytics: Analyze identity-related security risks.
- Risk-Based Alert Prioritization: Focus investigation on higher-risk activity.
- Advanced Threat Hunting: Support behavioral threat investigation.
Insider Threat & Data Exfiltration Detection
- Insider-Threat Management: Identify and manage insider-risk signals.
- Data-Loss Monitoring: Monitor suspicious data movement and potential exfiltration.
- Privilege-Abuse Detection: Identify potentially risky privileged activity.
- Policy-Violation Monitoring: Detect activity that may conflict with organizational policies.
- Investigation & Compliance: Support insider-risk investigations and compliance processes.
Identity Risk & Access Analytics
- Identity Threat Detection: Identify suspicious identity behavior.
- Privileged-Access Monitoring: Monitor high-risk and privileged access.
- Entitlement-Risk Visibility: Improve visibility into access risks.
- Access Review Support: Support identity and access review processes.
- Zero Trust Enablement: Strengthen identity-centric security strategies.
Security Automation & Incident Response
- Incident-Response Automation: Automate repetitive security-response activities.
- Playbook Orchestration: Standardize and coordinate response workflows.
- Case Enrichment: Add context and intelligence to security investigations.
- Threat Hunting: Support investigation and response workflows.
- Containment & Remediation: Accelerate coordinated response actions.
- Compliance Reporting: Support documentation and reporting requirements.
AI-Assisted SOC & Alert Investigation
- SOC Augmentation: Extend security analyst capabilities with AI-assisted operations.
- Alert Investigation: Accelerate investigation and analysis of security alerts.
- Incident Enrichment: Add behavioral and contextual intelligence.
- Response Acceleration: Help security teams move from detection to response faster.
- Analyst Productivity: Reduce repetitive investigation effort.
- Knowledge Continuity: Preserve investigation context across SOC operations.
Security Outcomes to Explore with ConsultEdge Global and Gurucul
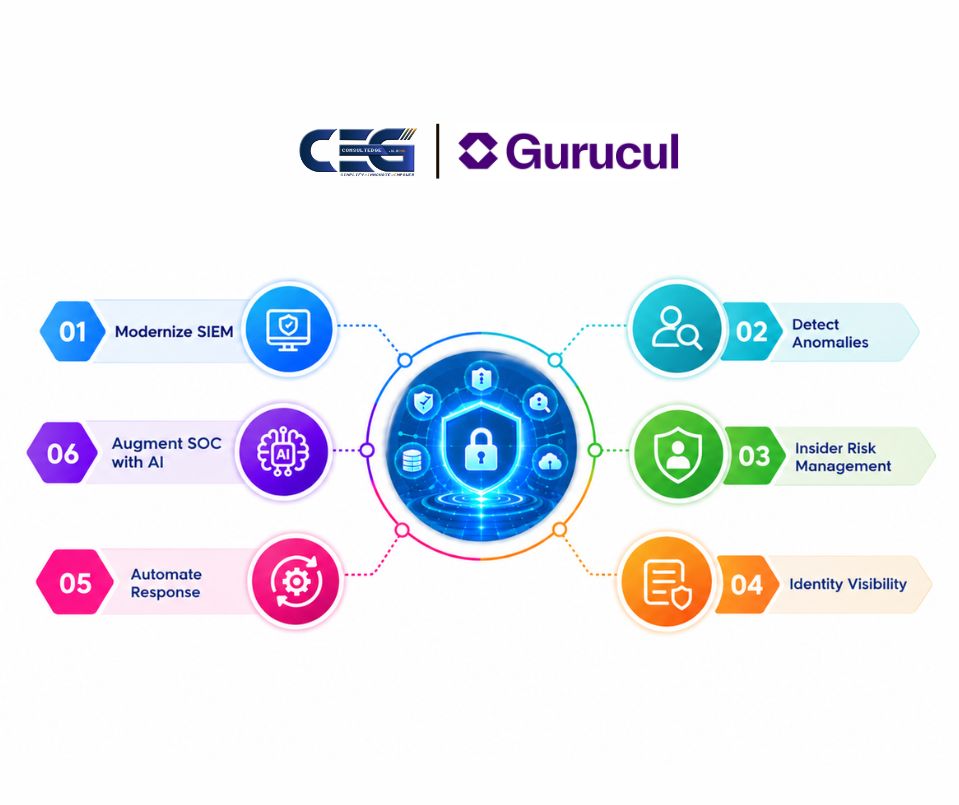
- Modernize Security Information & Event Management: Gurucul Next-Gen SIEM provides AI-powered security analytics, behavioral intelligence, and flexible data-management capabilities to support modern security operations.
- Detect Behavioral Anomalies: Gurucul UEBA helps organizations establish behavioral baselines, detect anomalies, and prioritize risks across users and entities.
- Strengthen Insider Risk Management: AI-powered insider-risk capabilities help organizations identify risky behavior, potential data exfiltration, privilege abuse, and policy violations.
- Improve Identity Risk Visibility: Gurucul Identity Analytics helps security teams understand identities, privileges, entitlements, and identity-related risks across hybrid environments.
- Automate Security Response: Gurucul SOAR helps automate triage, orchestrate response workflows, enrich investigations, and coordinate security actions.
- Augment SOC Teams with AI: Gurucul AI SOC Analyst helps security teams accelerate alert investigation, enrich incidents, and improve analyst productivity with AI-assisted security operations.
Why Choose ConsultEdge Global as Your Gurucul Solutions Partner?

Security Analytics Expertise
Our security consulting capabilities help organizations evaluate and implement AI-powered security analytics and behavioral detection solutions.
SIEM Modernization
We help organizations assess their existing security monitoring environments and support modernization toward advanced analytics-driven SOC operations.
UEBA & Insider Risk Expertise
We help organizations strengthen behavioral monitoring, insider-risk detection, identity analytics, and risk-based security operations.
Security Operations Automation
Our expertise supports security workflow automation, incident orchestration, investigation enrichment, and response optimization.
AI-Powered SOC Enablement
We help organizations explore AI-assisted security operations to improve alert investigation, contextual analysis, and analyst productivity.
Integration Across Security Environments
We support integration across security technologies including SIEM, SOAR, EDR, identity, cloud security, and other enterprise security platforms.
About ConsultEdge Global
Your Global Partner in Digital Transformation, Cybersecurity & Innovation
At ConsultEdge.Global, we help organizations modernize technology environments, strengthen cybersecurity, and improve IT operations through practical technology solutions.
Our cybersecurity capabilities span Security Operations, SIEM, SOC, Cloud Security, Identity Security, Data Protection, Threat Detection, Managed Security Services, and Security Consulting.
As a Gurucul Solutions Partner, we help organizations leverage Gurucul capabilities across Next-Gen SIEM, UEBA, AI-Powered Insider Risk Management, Identity Analytics, SOAR, and AI SOC Analyst.
We combine cybersecurity expertise with broader technology consulting capabilities to help organizations build stronger security operations, improve risk visibility, accelerate threat response, and support digital transformation.
ConsultEdge Global — Your Technology Partner for AI-Powered Security, Risk & SOC Transformation.
Contact Us
Frequently Asked Questions
Get answers to common questions about our Gurucul solutions and services.

